
See which vulnerabilities an attacker could chain together.
Eureka scans your code for SAST, SCA and secrets findings, then uses AI agents to threat-model it. The result is a list of attack scenarios: where an attacker starts, which vulnerabilities they chain together, and what they could reach. Each one gets a score, so you know what to fix first.
See an attack scenario in 20 seconds.
Scenario conditions, connected findings and potential impact.
20 seconds · No audio
Could this be exploited in your application?
A finding flags a potential weakness. Understanding the conditions around it helps you assess what an attacker could do and how seriously it could affect your application.
What would an attacker need?
Inspect the access and conditions the scenario assumes. Does it begin with an unauthenticated outsider, an existing account or another requirement your team needs to examine?
How could the weaknesses connect?
Follow the scenario back to the findings behind it. See how exploiting one vulnerability lets an attacker exploit the next.
What could be affected?
Understand the potential effect on data confidentiality, application integrity or service availability. Give the consequence a concrete place in the remediation discussion.
That context can support a more urgent assessment or a less urgent one. When your team finds that a required condition does not apply, you have a clearer basis for deciding how to handle the finding.
Low severity can still be part of a serious attack scenario.
Your team has reasons for accepting a finding. It needs privileged access. It looks unlikely to matter. There are more urgent issues in the queue.
But those decisions are often made one finding at a time.
What changes when exploiting one weakness lets an attacker exploit the next? An issue that looked reasonable to defer may deserve another look.
Eureka’s attack scenarios help your team examine those connections, inspect the assumptions, and decide what needs attention next.
condition
“Azure Defender tries to do this, but it's far more generic, and it is more infrastructure based, and I like this because this focuses on our code.”
Eureka threat-models your code for you.
Eureka uses AI agents to perform threat modelling on your code. The outcome is the list of attack scenarios you see in Eureka.
If your team already holds threat-model reviews, bring the attack scenarios into them.
A priority you can inspect. A decision you can explain.
The score directs attention. The scenario gives your team the reasoning to examine.
- 01PreconditionsWhat has to be true?EUREKA DOES THIS
See the access or conditions the scenario assumes. Understand whether it starts with an unauthenticated outsider, an existing account, or another requirement.
- 02Linked vulnerabilitiesHow could the attack progress?EUREKA DOES THIS
Follow the ordered steps back to the underlying findings. Give developers the issues behind the security concern, rather than a conclusion they must reconstruct.
- 03Potential impactWhat could be affected?EUREKA DOES THIS
Understand the potential effect on confidentiality, integrity, or availability. Make the consequence part of the prioritization conversation.
- 04Exploitability scoreWhere should we look first?EUREKA DOES THIS
Use the scenario score to focus review, then inspect the conditions and findings behind it. The score is Eureka's assessment of how exploitable an attack scenario is. The higher the score, the more likely it can be exploited, so fix it first. A low score means it is unlikely to be exploitable and can wait.
Watch the moment a finding becomes a different decision.
Start with the question your team needs to answer: “Why should we revisit this?” Follow the scenario through its conditions, linked findings, and potential impact.
Choose a step below to explore the example.
Check the starting conditions.
Open the scenario and inspect what an attacker would need. Here the scenario assumes an unauthenticated outsider and a Socket.IO endpoint an attacker can reach. That reachability is a required condition to confirm for your application, not proof of observed live exposure.
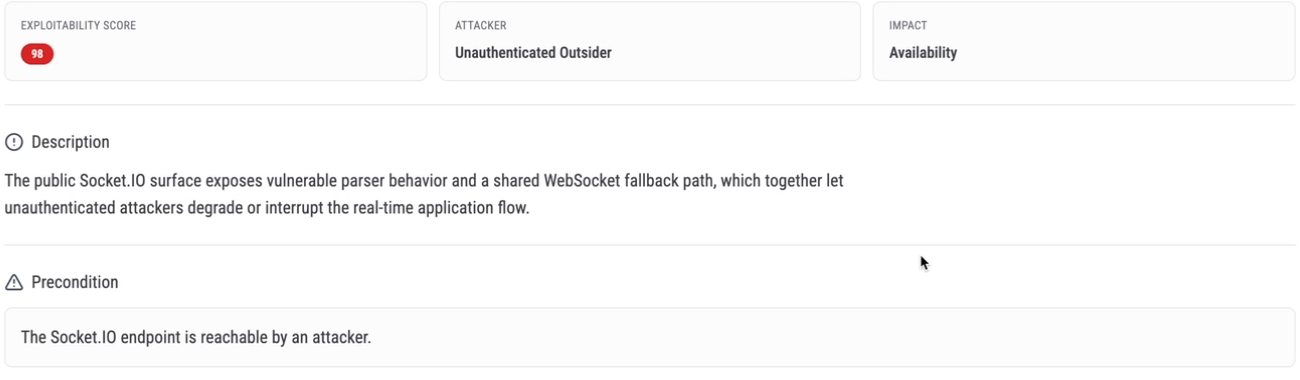
Demo environment. Scenarios model potential attacks; they do not execute exploits.
Give developers the reason behind the priority.
“Please fix this” is easier to act on when the team can see why it matters.
Use the per-finding attack-path score to focus review, then open the associated scenarios to examine the reasoning.
Which scenario?
See which attack scenarios the finding contributes to.
What conditions?
Inspect the access and conditions an attacker would need.
What potential impact?
Understand what could happen if the sequence holds.
Bring those answers into the conversation about what to investigate, fix or revisit.
Turn the next decision into a reviewable change.
Autofix works with GitHub repositories. Press the Autofix button and an AI agent writes the fix, Eureka scans to check the vulnerability is gone, and opens a pull request. You review and merge.
Less second-guessing in the conversations that matter.
Engineering leaders
Explain why security work deserves a place in the sprint. Give your team a reasoned priority they can understand and challenge.
Developers
Follow the security concern back to the underlying findings. Start the remediation conversation with the context you need.
AppSec teams
Revisit accepted findings in context. Explain the connection between weaknesses and their potential impact.
Attack path management, explained.
Practical answers about scenarios, scoring, threat modeling, and remediation.
An attack path describes a sequence of weaknesses and conditions that could lead to an adverse outcome. Examining the sequence can change how a team evaluates findings that looked less important in isolation.
The scenario brings together preconditions, ordered steps linked to underlying vulnerabilities, potential impact, and an exploitability score. Your team can inspect the reasoning and decide what to investigate or address.
Severity describes an individual issue. Scenario context adds the relationships and conditions that may make findings important together. It helps your team examine the potential sequence and outcome alongside the rating.
Eureka uses AI agents to perform threat modeling on your code. The result is the list of attack scenarios you see in Eureka: which vulnerabilities an attacker could chain together, and what they could reach. Eureka does not import, reconcile or update a threat model you already maintain.
They answer related questions. Reachability asks whether vulnerable code can be reached in an application’s context. An attack scenario describes a potential sequence, including its preconditions, linked findings, and impact.
No. These scenarios are modeled from analysis, rather than dynamic execution of an exploit. Use their assumptions and evidence to guide review alongside other testing appropriate to your application.
Yes. A finding judged acceptable on its own can deserve another look if it contributes to a meaningful scenario. Review the scenario’s conditions before changing the decision.
They describe different things. The scenario score applies to the modeled scenario; the per-finding attack-path score helps prioritize individual findings. Read the scenario details alongside the score.
That depends on the scenario, the change, and any remaining routes or conditions. Review the affected findings and updated status. A partial fix does not prove every relevant attack route is gone.
Autofix works with GitHub repositories. You press the button, an AI agent writes the fix, Eureka scans to check the vulnerability is gone and opens a pull request. You review and merge. Autofix does not fix every finding in an attack scenario at once, so check what is left.
See attack scenarios in action
Follow a scenario through its conditions, connected findings and potential impact.